
Before you start
Sign in as the user whose permissions the integration should use. Personal access tokens work across the companies that user belongs to; they are not limited to the currently selected workspace.
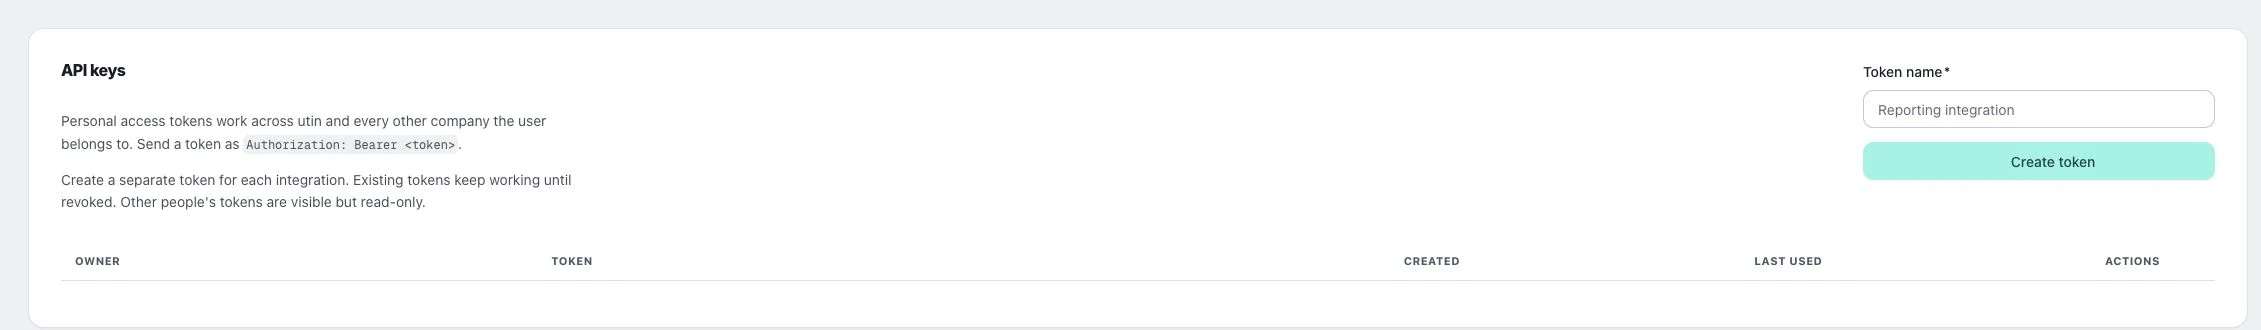
1. Create a named token
Open Agents & API → API keys, enter Token name and choose Create token. Use a distinct name for each integration so you can revoke one without interrupting the others.
2. Store the token securely
Copy the new token from the creation dialog into your integration’s secret storage. Treat it like a password. Send it in the HTTP header Authorization: Bearer <token>; do not put it in public URLs or source files.
3. Revoke an old token
Locate the token by name and use its revoke action. Read Revoke personal access token and confirm only the intended token. Creating a new token does not automatically revoke existing tokens.
Check the result
Use a read-only API request to confirm the intended integration works. After revocation, that token should no longer authenticate. Other people’s tokens may be visible but are read-only.
If something does not work
If you lose the secret, create a replacement and revoke the unused token. If access is denied, check both token validity and the user’s company permissions.